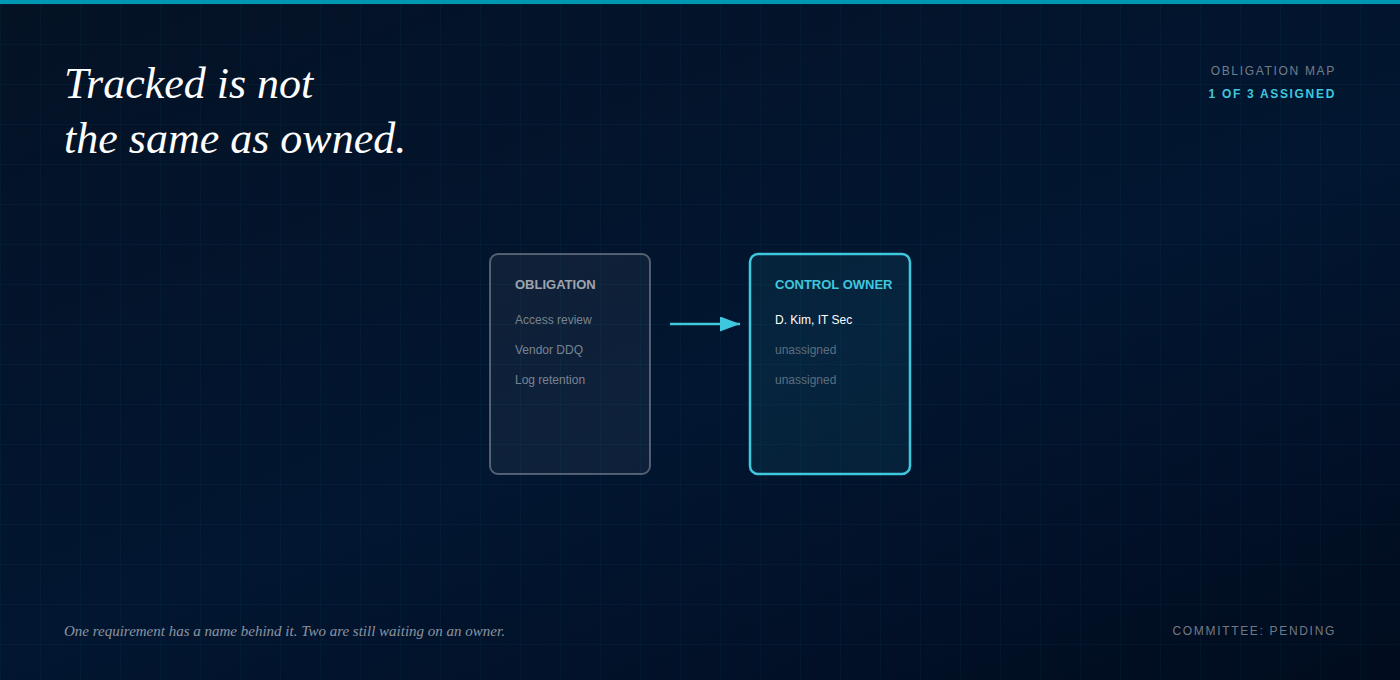
85% of executives say compliance requirements have become more complex, 97% of organizations now run at least two formal audits a year, and 38% report losing revenue or a competitive bid because they couldn't produce sufficient compliance evidence when asked.1 Pull any regulatory obligation from a compliance calendar and ask a simple question: who owns making sure this happens. In a surprising number of companies, the honest answer is a committee, which is another way of saying no one.
Tracking Is Not the Same as Executing
Compliance teams are good at knowing what the rules are. They're often much weaker on who's actually responsible for satisfying them day to day, because that responsibility usually sits with a business unit that didn't write the requirement and doesn't fully understand why it exists. The compliance team tracks it. The business unit executes it. When the two aren't in the same room regularly, the requirement drifts from “thing we do” to “thing we say we do.”
SOX Got This Right
SOX Section 404 is the clearest example of what happens when this works. It forces named control owners, documented testing, and a signature trail that makes ownership impossible to fudge. Compare that to a typical state privacy law requirement, where the obligation might be assigned to “the appropriate team” in a policy document and never touch an actual person's performance review. One of these gets audited into compliance. The other gets discovered during a regulator inquiry.
The Compliance Team Shouldn't Own Execution
Here's where I'll disagree with how most compliance programs are structured: treating the compliance team as the owner of every requirement is the mistake, not the fix. The compliance function should own the obligation register and the testing cadence. It should almost never own execution, because the people best positioned to actually satisfy a control are the ones doing the underlying work, not the ones tracking whether it got done.
Three Conditions for a Real Owner
- Knows the control exists.
- Has the authority to change the process it governs.
- Faces a consequence if it lapses.
Miss any one of the three and you have a name in a spreadsheet cell, not an owner. Most gaps trace back to the second condition. Someone gets assigned ownership of a requirement they have no power to actually change.
Frequently asked questions
Should compliance ever own a control directly?
Occasionally, for controls with no natural business-unit home, like whistleblower hotline administration. Everywhere else, ownership should sit with whoever runs the underlying process.
How do we know if a control owner has real authority?
Ask them to change the process the control governs without escalating. If they can't, they're a reporter, not an owner.
What's the fastest way to find unowned obligations?
Cross-reference your obligation register against your org chart. Any requirement that maps to a department instead of a person is a gap waiting to surface during the next audit.
Map Every Obligation to a Name With Real Authority
Devensa AI's vCCO vOfficer maps every regulatory obligation to a named control owner with the authority to act on it, not just a department listed in a tracker.
If a regulator asked for evidence a specific control operated today, could your team produce it before the meeting ended?
Schedule a demo with our team at info@devensa.ai, or request early access to the Governance Readiness Assessment, coming to devensa.ai.
Sources
- NAVEX, State of Risk and Compliance Report 2026, cited via Bright Defense. https://brightdefense.com/resources/compliance-statistics