

Alyssa O'Brien
CEO, Devensa, Inc.
Articles by Alyssa
Risk Management
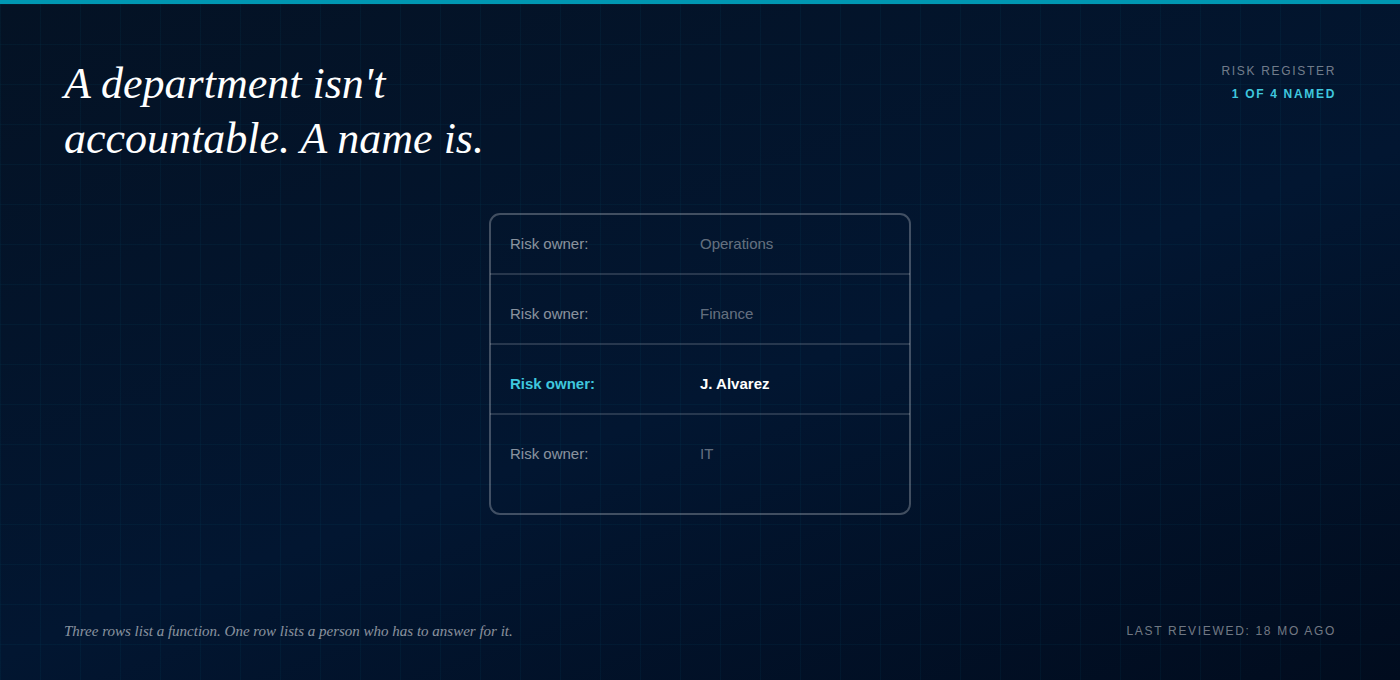
What Happens When Risk Ownership Isn't Assigned
Firms without board-level risk visibility are 20% more likely to face major risk events. See what happens when a risk register lists departments instead of names.
Cybersecurity
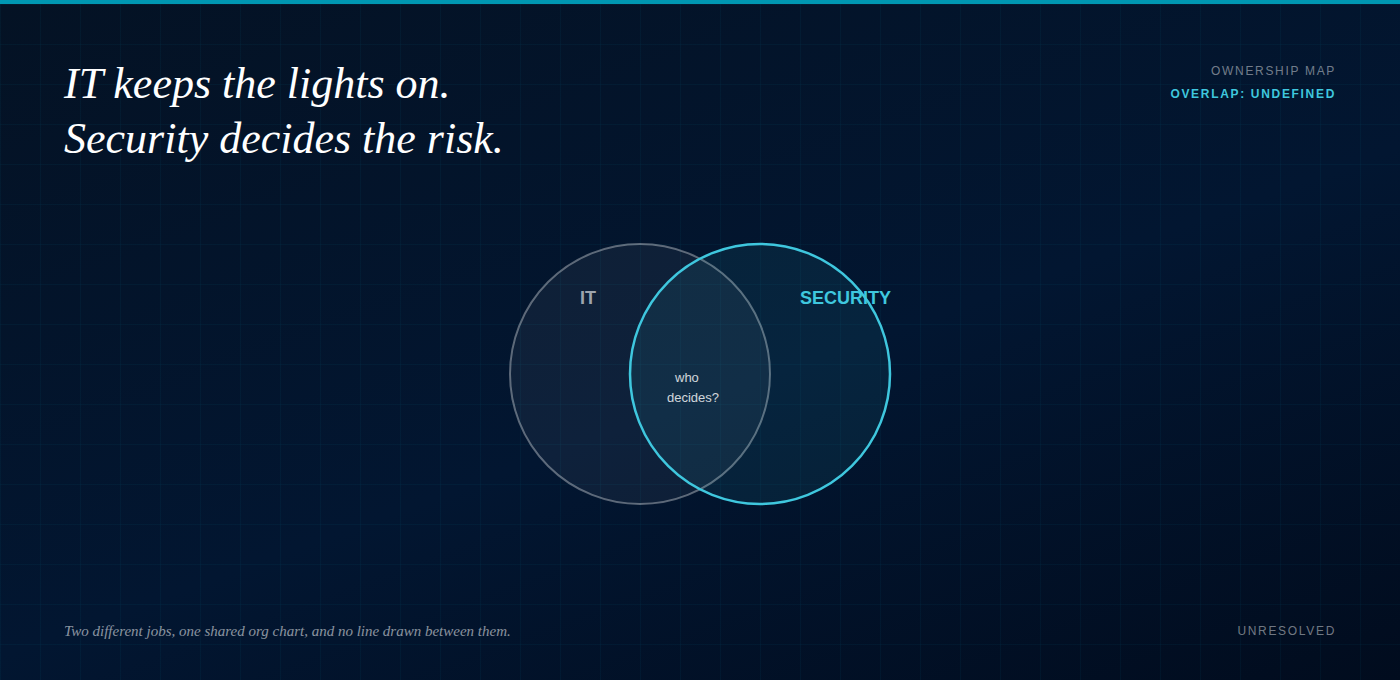
Security Ownership: Why “IT Handles That” Is Usually Wrong
IT and security get treated as one job. They aren't. See where that confusion actually breaks, and what the 2026 DBIR shows about the cost of unassigned risk decisions.
AI Governance
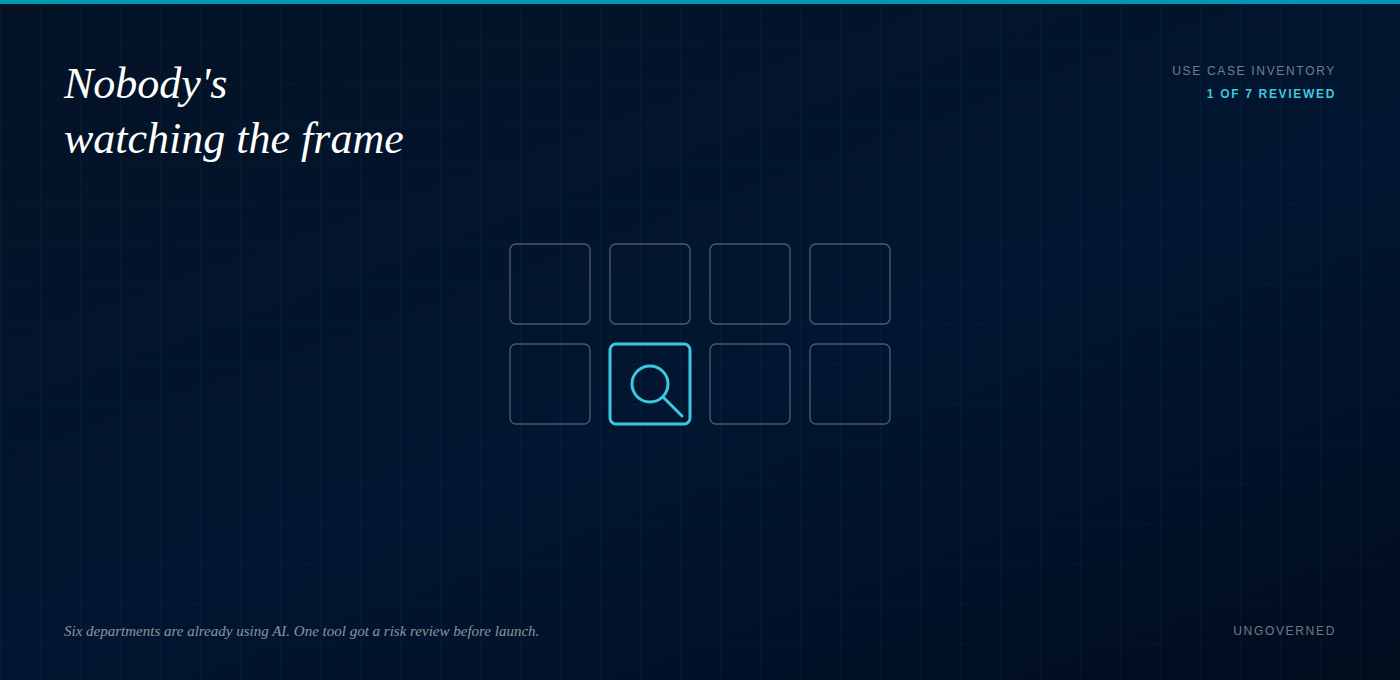
What Happens When No One Owns the AI Policy
A policy without a named owner is a document, not a control. See what shadow AI adoption looks like without real governance behind it.
Data Governance
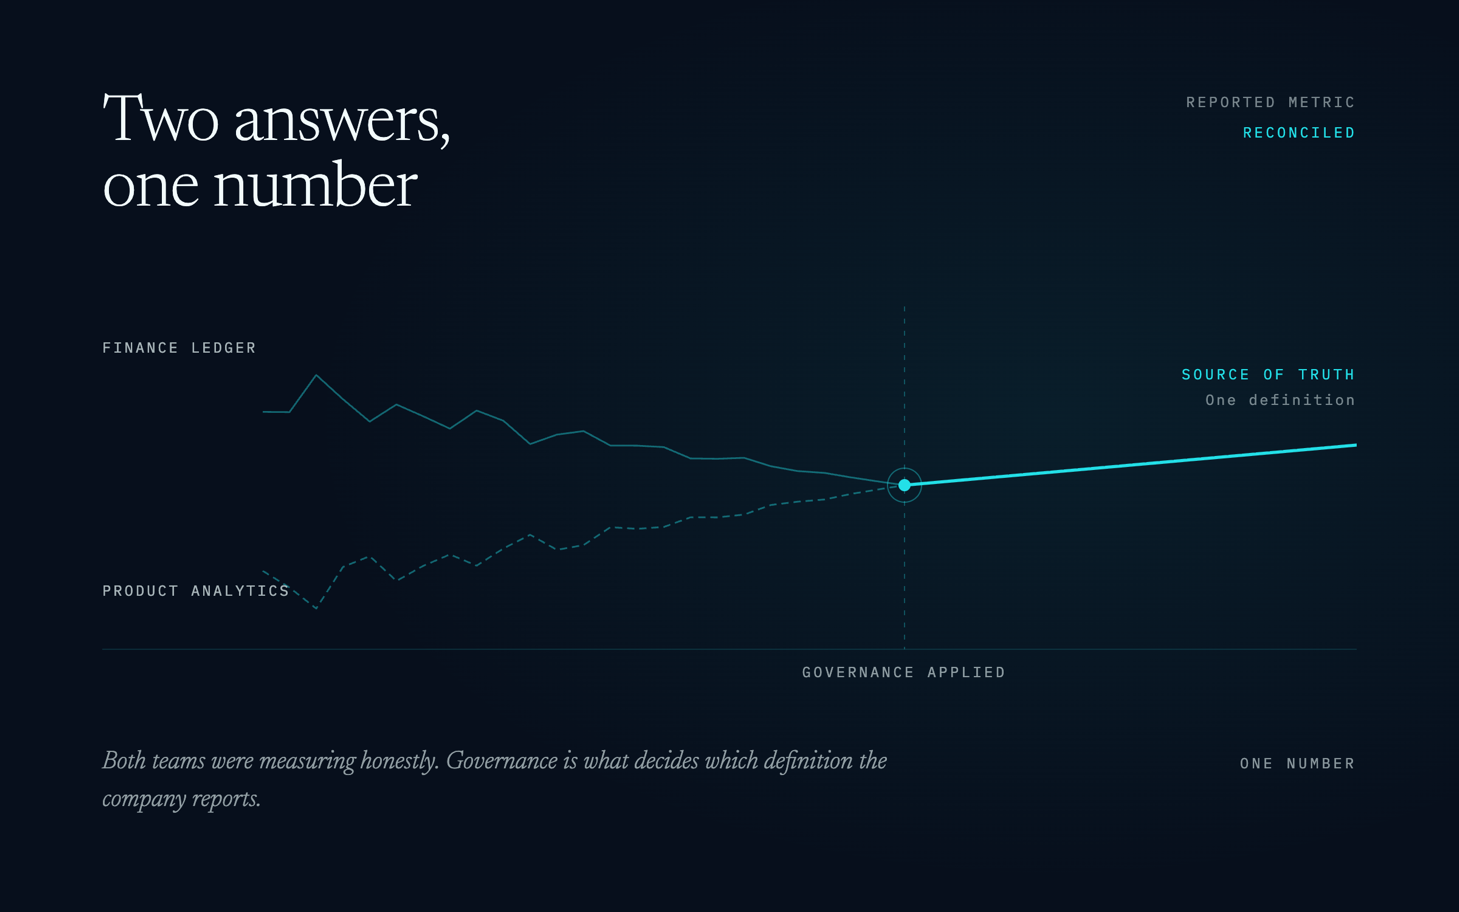
Five Data Findings That Repeat in Every Audit
Poor data quality costs the average company $12.9M a year. See the five data findings that repeat in audit after audit and what actually fixes them.
AI Governance
Five Signs an AI Deployment Has No Governance Behind It
No model inventory, no owner when things go wrong, no real review before approval. See the five signs an AI deployment has no governance behind it.
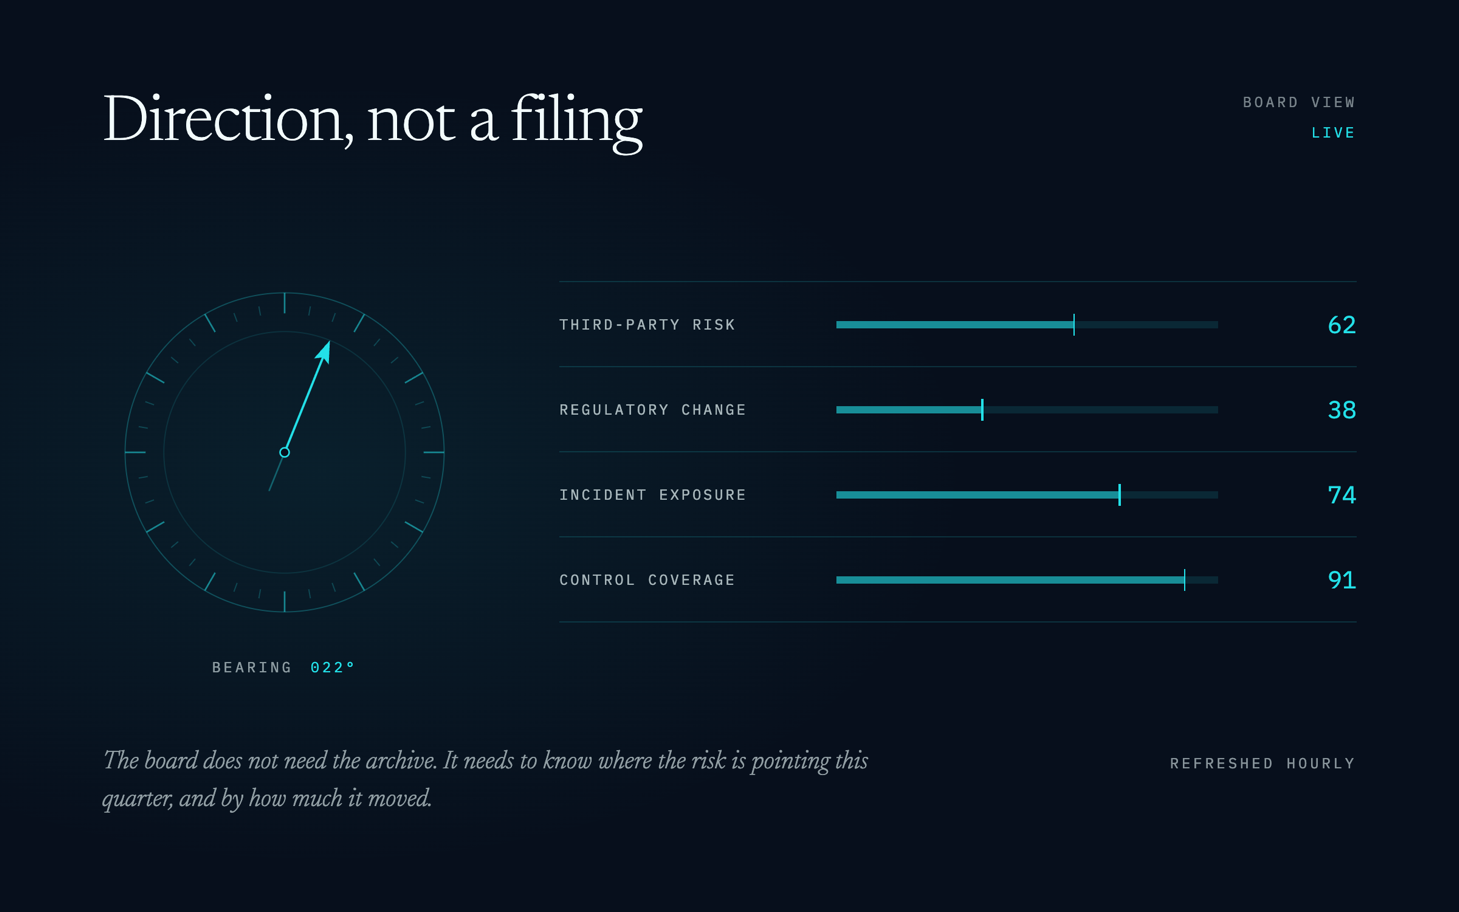
Risk Management
Five Signs Your Risk Register Is a Filing Cabinet, Not a Tool
Firms without board-level risk visibility are 20% more likely to face major risk events. See the five signs a risk register has stopped being a tool.
Privacy
Five Privacy Findings That Show Up Long After the Policy Was Signed
A privacy policy is a snapshot, not a subscription. See the five privacy findings that surface long after the policy was signed and board-approved.
Compliance
Five Controls That Always Pass Review and Always Fail in Practice
A control can pass a SOC 2 exam for years and still fail the moment it matters. See the five controls that consistently pass review and fail in practice.
Cybersecurity
Five Security Findings That Show Up in Every Audit
The same five cybersecurity gaps show up in audit after audit. See why they keep recurring and how continuous, AI-monitored governance closes them.